Worklog for task "Organize integration of the new frontend with the existing MODX backend"
Now, in our new GraphQL API, we need to test proxying and request processing.
I've added a resolver draft and right now I can check whether requests are reaching the MODX handler and whether we are getting a response back.
Here I see a correct response in JSON format stating that I don't have access when trying to create a request.
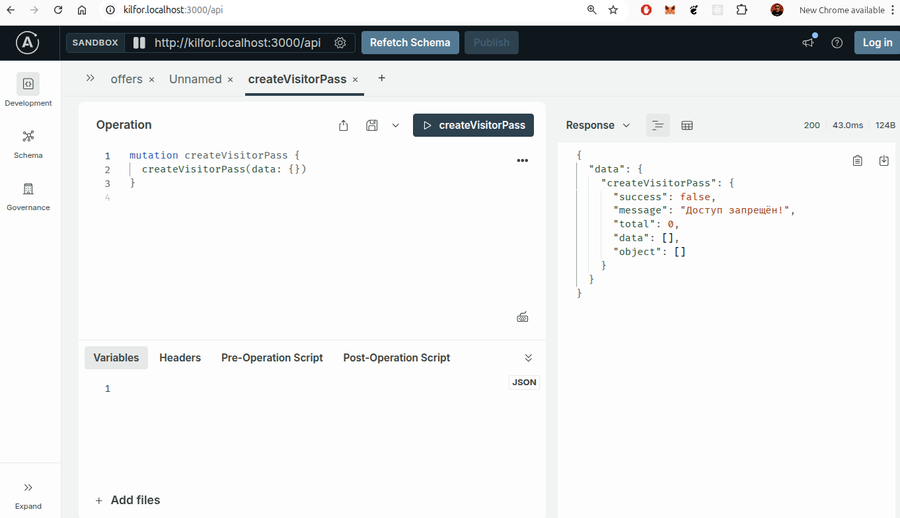
This means the request itself is sent to the MODX site and processed correctly. Now we need to add user authorization.
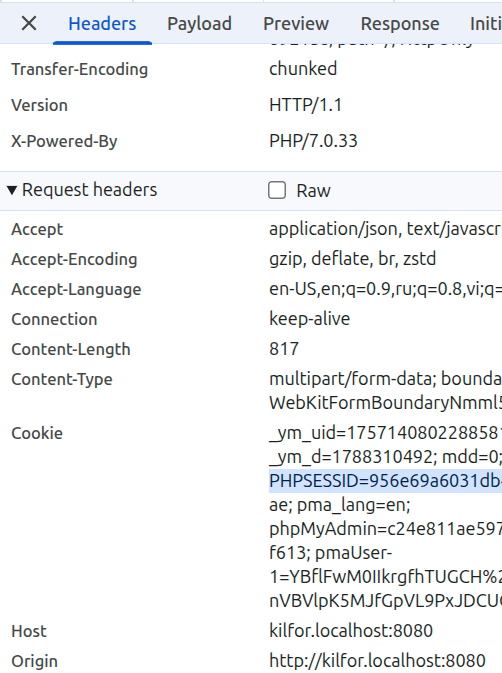
In the personal account, we need to find the current session cookie. It can be found either in the request headers
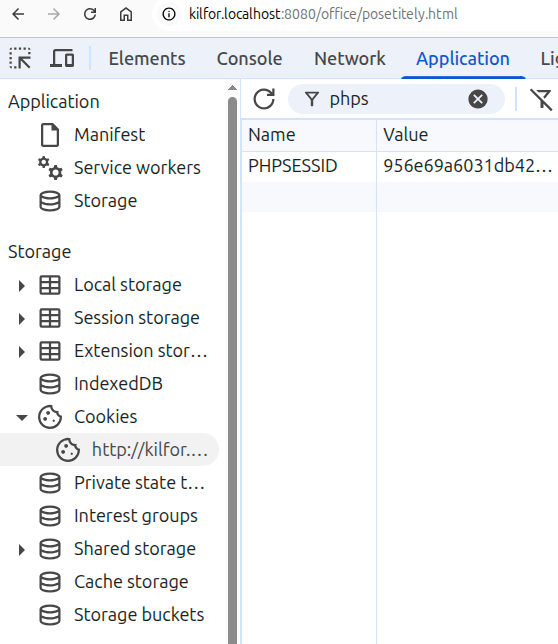
or even simpler - go to the Application tab and look in the general list of cookies.
Now this cookie can be added as a custom header in the GraphQL playground of our new API.
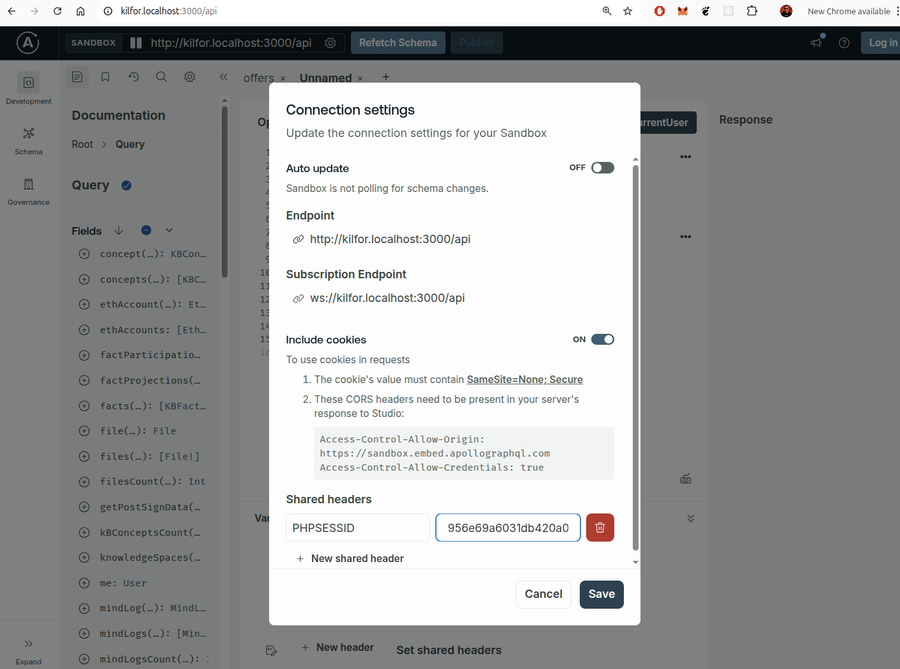
Now, by sending a request with the authorization cookie, we get a response with a list of errors during form data validation.
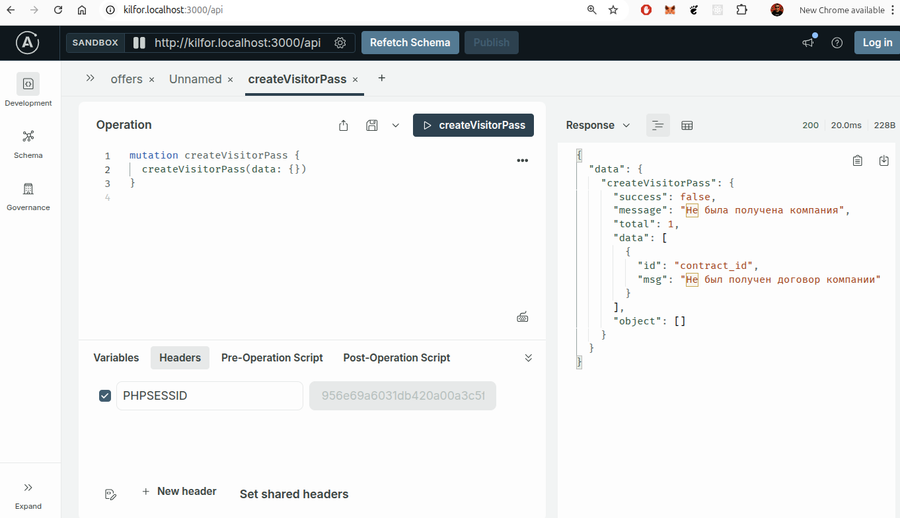
That's it. We can consider the API framework itself ready. All that remains is to describe the request and response parameters, and we can hook it up to the frontend.
Define and implement a secure interaction layer between the new frontend and MODX data and functions.